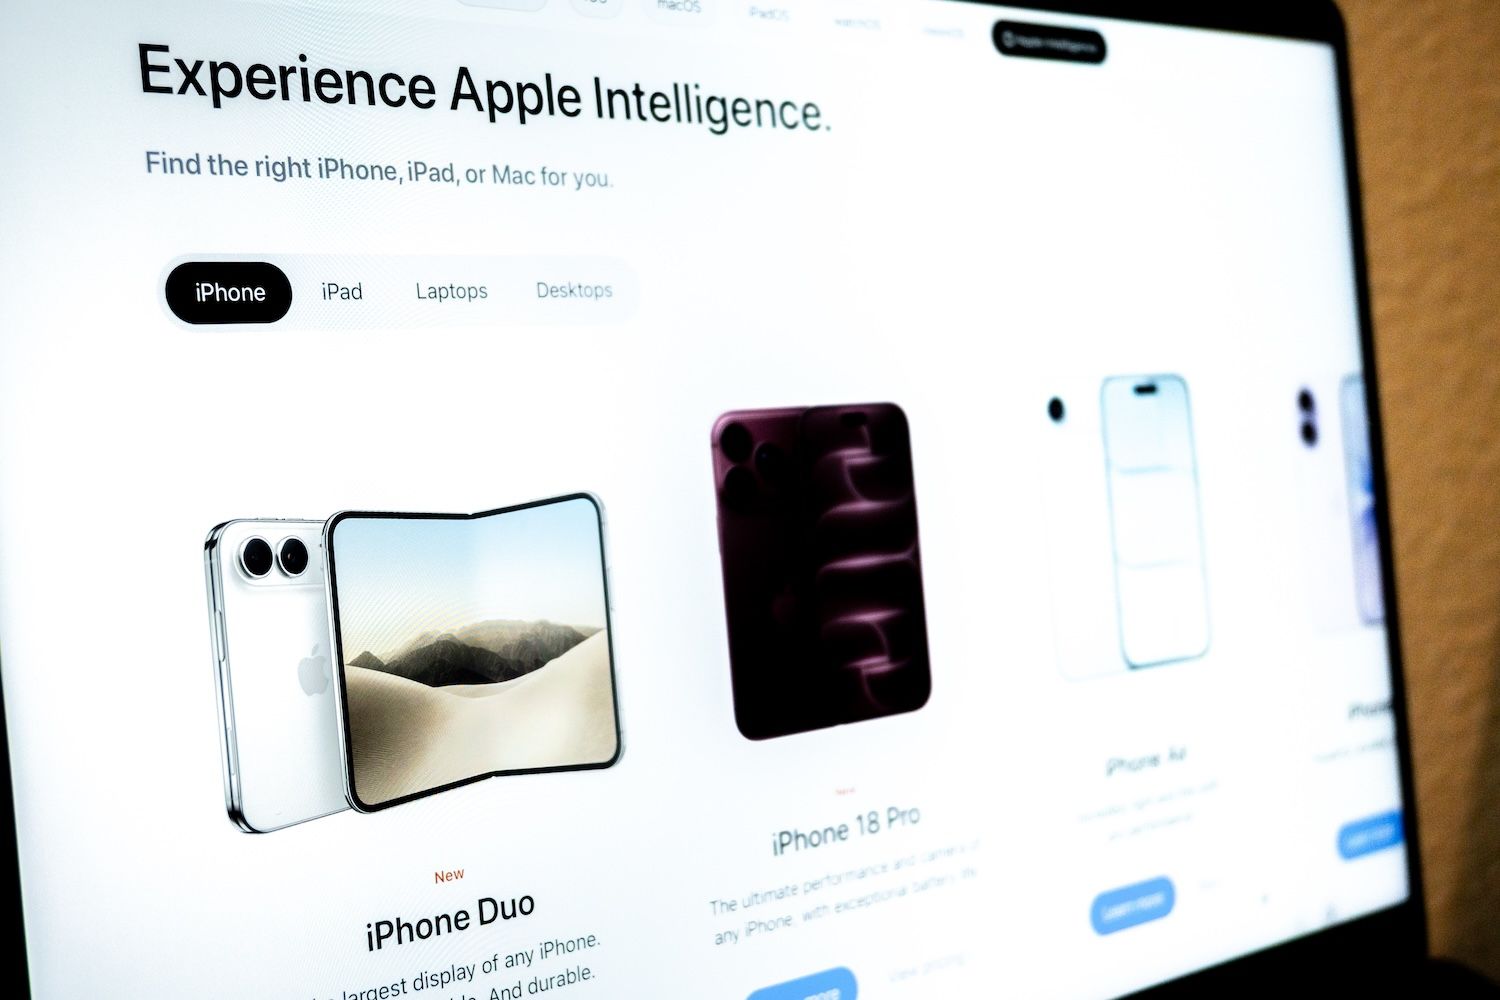
Security researchers found a fake AppleiPhone Duo preorder page using a $500 voucher lure to target vulnerable iPhones and crypto wallets before Oct. 16 preorders. Key Points: Exploit attempt
Security researchers found a fake AppleiPhone Duo preorder page using a $500 voucher lure to target vulnerable iPhones and crypto wallets before Oct. 16 preorders.
Key Points:
- Exploit attempt can start when a vulnerable iPhone opens the page
- Payload targets crypto wallets, keychain credentials, notes and other personal data
- Apple says updated devices are protected against the reported DarkSword attacks
iPhone Duo Scam
Security researchers at Malwarebytesfound the Apple-style page while tracking fraud tied to the iPhone Duo launch, according to findings published Sep. 29 and reported by 9to5Mac a day later.
The site offers a $500 “Authorized Partner Exclusive” voucher and AppleCare+ coverage. Official iPhone Duo preorders do not begin until Oct. 16.
Malwarebytes said the fake page also lists device sizes and colors that do not match Apple’s lineup, while several policy links on the site do not work. The exploit attempt begins before a visitor submits anything. Malwarebytes also said the page uses the leaked DarkSword exploit chain to probe vulnerable iPhones, then tries to load a separate payload that can collect device information, Apple Notes and saved keychain credentials.
Also Read:Polymarket Kyiv Strike Bets Show $124,000 Volume, But Two Trades Explain It
Malwarebytes Wallet Risk
The payload searches for crypto wallet apps including MetaMask, Phantom, Trust Wallet, Coinbase Wallet, Exodus and Tonkeeper, and can attempt to upload wallet files, credentials and photo thumbnails if its connection to the attacker’s server succeeds.
Researchers also found code aimed at messages, contacts, call history, voicemail, email, calendar entries and cached location data, while the payload can contact its server for additional instructions.
Malwarebytes said it analyzed the captured code but did not test it on an iPhone or observe data leaving a device, a limitation that means the researchers confirmed the attack logic rather than a successful theft from a victim.
Google disclosed DarkSword in Mar. 2026, and Apple patched the reported vulnerabilities later that month. iVerify estimated at the time that up to 270 million devices were running targeted iOS versions, but Malwarebytes said the figure is not current and this page’s exact vulnerable range is unconfirmed.
Read Next:Rogue AI Agents Force OpenAI Into A 50-Petabyte Search Of Its Own Records