Markets2 min read
First Official $BIG Buy-Back Completed
BIG Indie Games has completed its first official $BIG buy-back, purchasing approximately $565 worth of $BIG from the open market. This marks the beginning of an important part of the BIG Indi
Blockchain security firm SlowMist issued an alert reporting that Aave v3's Loop Safe Module was exploited, with approximately 114.09 ETH stolen. The alert identifies the Loop Safe Module as t
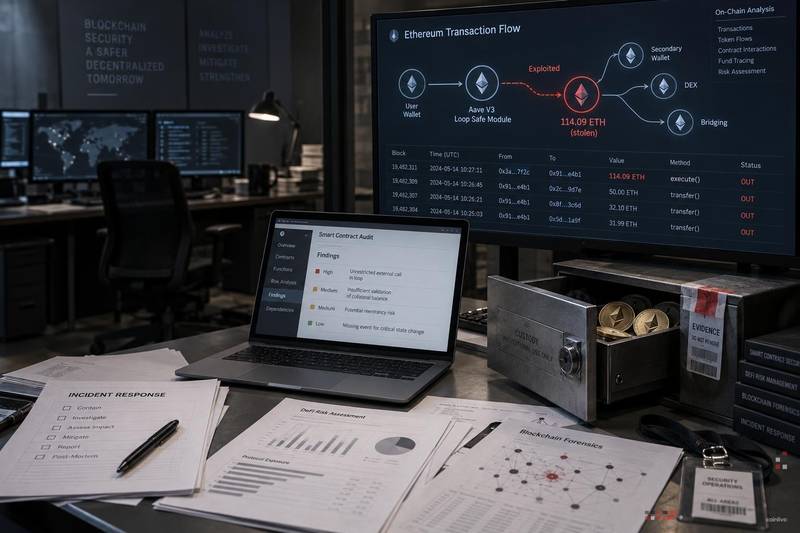
Blockchain security firm SlowMist issued an alert reporting that Aave v3's Loop Safe Module was exploited, with approximately 114.09 ETH stolen. The alert identifies the Loop Safe Module as the targeted component, though SlowMist has not detailed the attack vector, attacker identity, or current remediation status.
SlowMist, which previously flagged the Liquid Network exploit that minted 3,998 L-BTC, named the Loop Safe Module within Aave v3 as the exploited component. The firm reported the theft at approximately 114.09 ETH. No transaction hash has been included in the available alert details, so on-chain verification remains pending at time of publication. For related coverage, see Ripple reveals XRPL privacy and AI-agent upgrades in Seoul.
Aave v3 is one of the largest decentralized lending protocols by total value locked. A module-level exploit differs from a core protocol breach, but it still carries direct financial risk for users interacting with that specific component. Aave users should monitor official Aave governance channels and SlowMist's security feeds for any pause instructions or contract advisories.
Module-level vulnerabilities in DeFi protocols can affect users who believe they are insulated by the broader protocol's audited core contracts. The reported 114.09 ETH loss demonstrates material financial impact, even if core Aave v3 logic is unaffected. Aave has previously seen significant capital flows, including 20,000 ETH moved from Bitfinex to Aave, illustrating the scale of assets the protocol manages.
The scope of broader exposure beyond the reported figure is unconfirmed. Whether the exploit is ongoing or closed, and whether additional user funds remain at risk, are unknowns until Aave or SlowMist publish a formal postmortem. The current ETH price determines the precise dollar value of the loss, which has not been confirmed in official figures.
This is not the first module-linked theft to surface recently. A stolen NuNet key minted 408.5M NTX in a separate incident, illustrating the range of attack surfaces across DeFi infrastructure. In each case, a targeted component outside main contract logic proved to be the entry point. Users should not assume the incident is contained until an official statement confirms it, a pattern also seen after the $42M theft that led Bo Shen to offer a 20% recovery bounty.
Disclaimer: This article is for informational purposes only and does not constitute financial or investment advice. Cryptocurrency and digital asset markets carry significant risk. Always do your own research before making decisions.
Read original article on coinlive.me