The XRP Ledger is adding granular transaction permissions that allow account holders to delegate limited signing authority to third parties, services, or automated systems without exposing th
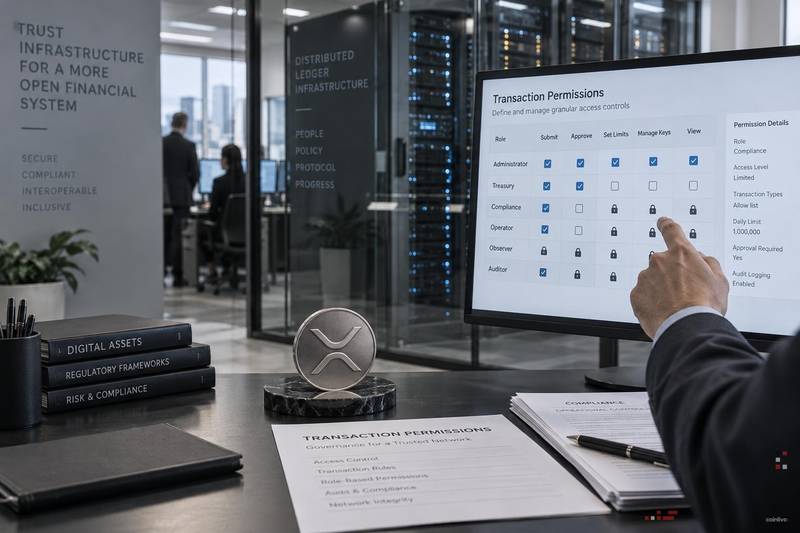
The XRP Ledger is adding granular transaction permissions that allow account holders to delegate limited signing authority to third parties, services, or automated systems without exposing the account's primary signing key. The update targets a core operational security problem: granting routine transaction access to staff or applications while preserving full account control at the owner level.
TLDR KEYPOINTS
- XRP Ledger is introducing per-transaction-type permission controls for account delegation.
- Delegated credentials can be scoped to specific transaction actions, keeping the primary signing key out of operational workflows.
- Granular permissions separate routine access from full account authority, reducing single-point-of-failure exposure.
Why Primary Signing Keys Create a Single Point of Failure
A primary signing key represents unrestricted authority over an XRP Ledger account. Sharing it with any service, employee, or automated system means a single compromise can drain or misuse the entire account. For businesses running treasury operations or payment flows, that exposure scales directly with the number of parties who touch the key. For related coverage, see Five Bitcoin Indicators Turn Bullish for First Time Since 2025.
The granular permissions model addresses this by allowing account owners to issue constrained credentials. An authorized party receives the ability to perform only defined transaction types, not blanket account access. If that credential is compromised, the blast radius is limited to the permitted scope rather than the full account. For related coverage, see Thailand to Allow Bitcoin & Ethereum ETFs From October 16.
Scoped Access and Separation of Duties
Scoped access draws on a well-established principle in enterprise security: least privilege. Each delegated credential is bound to a defined set of permitted actions. A payment processing service might receive permission to send transactions within set parameters, while a treasury team retains exclusive authority over account reconfigurations or large transfers. For related coverage, see Thailand SEC Bitcoin & Ether ETF Rules Take Effect Oct. 16.
Permissions under this model are not permanent by design. Account owners should treat them as operational configurations to be reviewed, updated, and revoked as team structures, service integrations, or risk tolerances change. A stale permission granted to a vendor or service that is no longer active is its own category of risk. For related coverage, see Bitcoin Drops $7,000 in Three Days: Market Correction.
Who Benefits and What to Watch Before Relying on It
The clearest use cases are businesses that need staff or automated systems to execute recurring, limited transaction tasks without handing over a master credential. Wallet developers and application builders can also use scoped permissions to reduce the need for full-key custody in their infrastructure, lowering their own liability surface if systems are breached.
XRP has been gaining institutional attention alongside broader asset-class developments, including XRP's presence in spot ETF discussions alongside Bitcoin. Protocol-level access controls like this are a prerequisite for the kind of institutional treasury and custody integrations that make those products operationally viable.
Before relying on the capability, teams should verify which specific transaction types fall within the permission scope, confirm how revocation is handled on-ledger, and establish internal processes for auditing active delegations. The update improves the security architecture for XRPL account management, but it does not replace disciplined key management practices. Permissions that are misconfigured, left unreviewed, or granted too broadly recreate the same exposure the feature is designed to prevent.
Additional source references: source document 1, source document 2.
Disclaimer: This article is for informational purposes only and does not constitute financial or investment advice. Cryptocurrency and digital asset markets carry significant risk. Always do your own research before making decisions.
Read original article on coinlive.me